

How access fits together
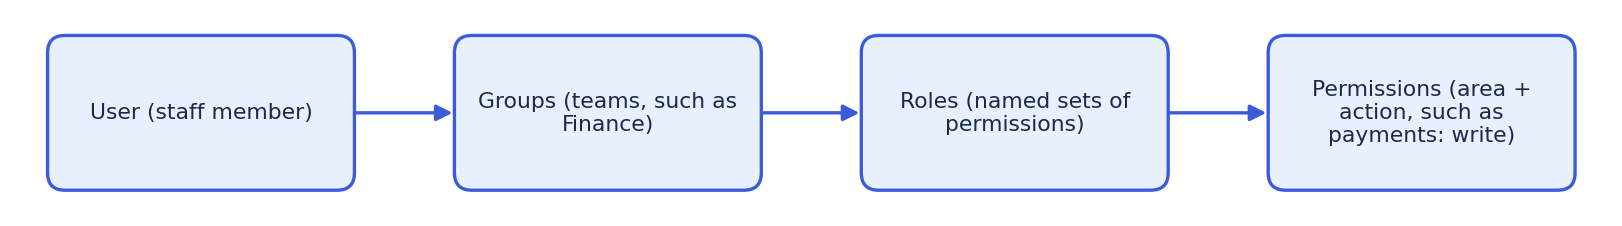
Users, groups, and roles
- Users are staff members.
- Groups are teams, such as Finance or Code Enforcement. A user can be in several groups.
- Roles are named sets of permissions, such as Finance Admin. You attach roles to groups, not to people.
Permissions
A permission pairs an area of the product, such as cases or payments, with an action:- read: see it.
- write: create or change it.
- delete: remove it.
- export: download it.
Access is per organization
If your workspace has several organizations, such as separate departments, access is checked for the organization you’re working in. A person can have access in one department but not another. A Cross-Organization Role is a role one organization shares with others in the same workspace. The owning organization controls its name and permissions.Role templates
When you create a role, you can start from a template and adjust it. Templates include Staff, Finance Admin, Knowledge Base Manager, Account Provision, Org Management, and Super Admin.Groups managed by SSO
If your organization uses single sign-on (SSO), your identity provider can control who is in a group. These groups show a lock icon. You can still rename them and change their roles, but you add or remove members in the identity provider.Permissions aren’t the only reason something is missing
Polimorphic turns some features on for each organization. If a coworker sees something you don’t and you have the same roles, the feature may not be on for your organization.Example: a town finance office
A town has a Front Counter group for clerks and a Finance group for the treasurer’s staff.- Front Counter has a Staff role. Clerks can work cases, update contacts, and take payments.
- Finance has a Finance Admin role. Finance staff can also see payout batches and manage payment types, and they can read cases and contacts.